The Bottleneck: Why AI Agents Struggle with the Browser
Developers working with modern AI coding assistants (Google Antigravity, Claude Code, Cursor, Codex) inevitably hit a common barrier: the agent needs to interact with an authenticated web dashboard.
Common real-world scenarios include:
- Reviewing Google Search Console or Bing Webmaster indexing statistics.
- Inspecting and approving open pull requests on GitHub.
- Verifying DNS record propagation in Cloudflare.
- Testing user interface changes inside an internal administrative staging dashboard.
Standard tooling typically launches a headless browser instance via Puppeteer or Playwright. However, that blank profile lacks your developer logins, session cookies, and extensions. It immediately halts at a two-factor login screen, leaving the agent stranded.
Synthetic DOM events create an additional hurdle. Triggering document.querySelector('button').click() produces an event marked with isTrusted: false. Modern React and Vue single-page applications frequently discard synthetic clicks, preventing dropdowns and modals from opening.
The Solution: Chrome DevTools Protocol (CDP) Bridge Architecture
Rather than transmitting session cookies to cloud proxies or re-authenticating repeatedly, we connect the agent directly to the developer's running Chrome browser.
The architecture comprises three lightweight components:
- Chrome Extension (Manifest V3): runs locally in your browser, communicates with the daemon over WebSocket, and utilizes
chrome.debuggerto dispatch engine-level CDP commands. - Local Daemon (Python): binds exclusively to
127.0.0.1:8766. It orchestrates agent commands, handles tab management, and saves annotated snapshots. - CLI Interface
br.py: a streamlined command-line tool that coding agents execute directly from terminal turns.
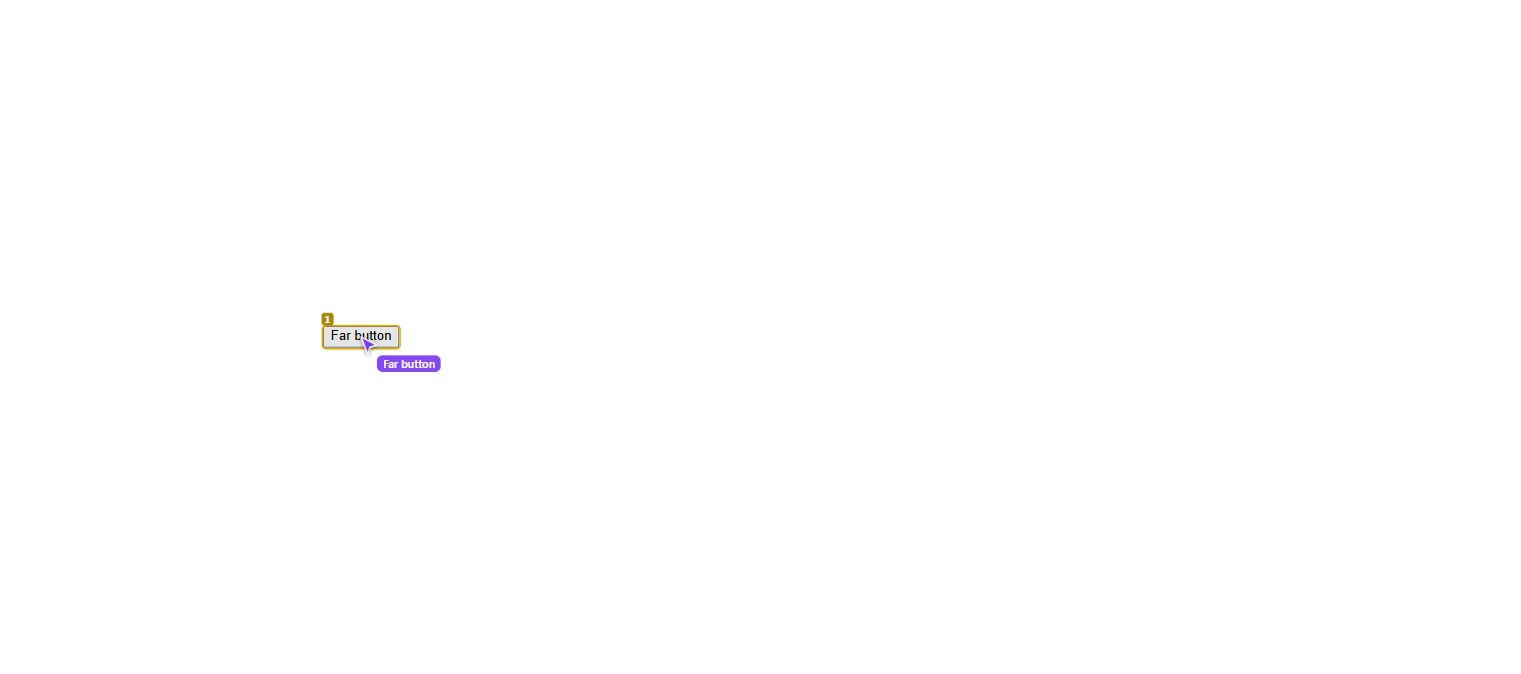
What the agent sees after shot: every button and field gets a number, the purple arrow shows where its cursor is.
Agent Vision: Why Numeric Labels Beat CSS Selectors
Directing an agent with fragile selectors such as button.btn-primary.flex.mt-2 frequently breaks upon minor markup refactors.
Agent Chrome Bridge adopts visual element indexing:
- Running
python server/br.py lookscans visible DOM nodes and tags every interactive control with a clean index:[1],[2],[3]. - The agent receives an unambiguous inventory:
[14] button "Create repository",[16] input:text "Repository name". - To act, the agent executes
python server/br.py click 14. - If the layout shifts, the subsequent
lookrefresh recalculates indices automatically, preserving test stability.
Real-World Example: Verifying Search Indexing
Consider an agent tasked with auditing indexing health in Google Search Console:
- The agent executes
python server/br.py open https://search.google.com/search-consoleto open the dashboard in a background tab. - It runs
python server/br.py lookand identifies:[5] button "Performance",[8] a "Pages". - It dispatches
python server/br.py click 8via trusted coordinates. - It captures
python server/br.py shotto inspect the indexed page trend chart.
The task completes in seconds without prompting the user for one-time passcodes or re-authentications.
Security Boundaries and Best Practices
Granting AI agents browser access demands disciplined operational hygiene:
- No Passwords in Context: agents must never be instructed to enter credentials or recovery keys. The developer authenticates manually; the agent assists within open sessions.
- Payments & Bot Gates Require Humans: the bridge does not bypass CAPTCHAs or Cloudflare challenges. The bundled
AGENT_RULES.mdtells the agent to stop at checkout, CAPTCHA or sign-in screens and ask you. - Loopback Isolation: the server listens on 127.0.0.1 only and rejects requests coming from web pages (Origin and Host checks). Websites cannot drive the bridge through your browser.
Conclusion
Browser automation for AI coding agents can be lightweight and safe. Leveraging Chrome DevTools Protocol allows developers to automate complex browser chores while keeping complete control and credentials firmly on local hardware.
Frequently asked questions
Why is standard headless Playwright insufficient for daily AI agent workflows?
Playwright starts a clean, isolated profile with no stored cookies, bookmarks, or browser extensions. Whenever your agent needs to check Search Console impressions, review a GitHub pull request, or modify Cloudflare DNS settings, it hits login barriers and two-factor authentication (2FA). Operating inside your real Chrome gives the agent immediate access to your existing authenticated sessions.
What are trusted browser events and why do they matter?
In web browsers, mouse and keyboard events have event.isTrusted=true only when initiated by a human user or generated via Chrome DevTools Protocol at the browser engine level. Synthetic events (like element.click() or custom dispatchEvent) have isTrusted=false, and modern frameworks (React, Angular, financial portals) actively ignore them to block bots.
Is it safe to run a local bridge daemon on my machine?
The daemon listens strictly on loopback address 127.0.0.1 (localhost) and never exposes ports to external networks. Furthermore, incoming WebSocket connections validate the Origin header and only accept Chrome extensions, while HTTP requests coming from web pages are rejected. A website open in your browser cannot send commands to the local port. While the server runs, any program on your computer can use it, so stop it when your agent is idle.
Can the agent expose passwords or trigger unauthorized payments?
The bridge does not bypass CAPTCHAs, and the bundled AGENT_RULES.md tells the agent never to type passwords or approve payments. Authentication is always completed manually by the user, after which the agent operates within the authenticated tab strictly on the delegated task.
How does the agent select target elements without brittle CSS selectors?
The look command scans the active viewport, identifies all interactive elements, and assigns them deterministic numeric tags: [1], [2], [3]. The agent simply invokes click 2, completely bypassing complex obfuscated class names or dynamic CSS hashes.